
Coldcard Code Bug Leads to $100M Theft in Digital Assets
Key Facts
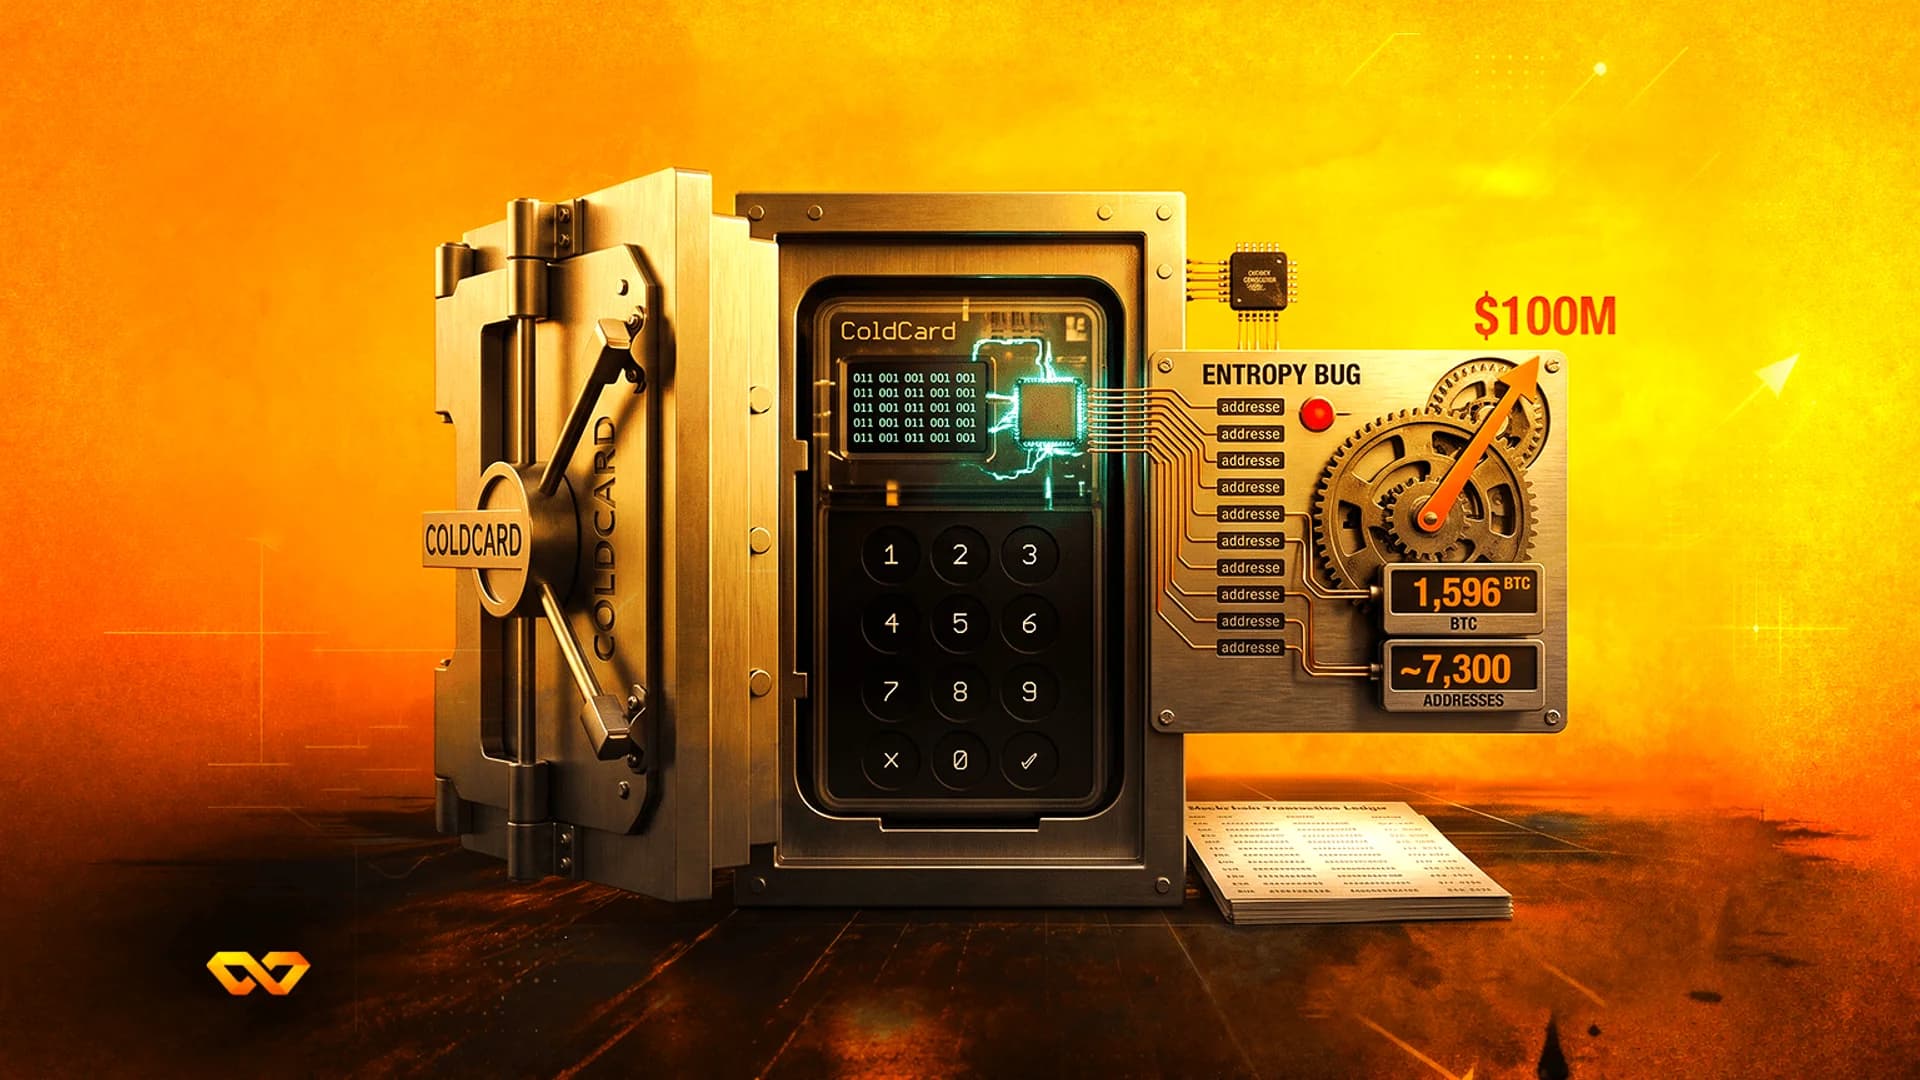
Amid rising reliance on cold storage solutions to protect digital assets, reports have emerged of a critical security flaw in Coldcard wallets. According to reports, a long-unnoticed bug in Coldcard’s source code led to the theft of funds valued at approximately $100 million. Attackers exploited this firmware vulnerability to compromise digital assets stored on these hardware devices, which were previously marketed as ultra-secure solutions.
This crisis raises serious concerns regarding security standards within the crypto hardware wallet sector, particularly as the software bug provided a multi-year window for attackers to undermine device integrity. This exploit has resulted in a significant breach of trust for a major hardware wallet provider, potentially impacting investor sentiment toward self-custody solutions in the near term.
Traders are looking ahead to major catalysts, including the U.S. Consumer Price Index (CPI) release on August 12, 2026, which may influence broader market liquidity and risk appetite for alternative assets.
Latest Updates · 2
- Notable·
Update: Further investigations have revealed that the vulnerable Coldcard firmware was initially released in 2021, implying the flaw remained active for five years. This extended timeline suggests the theft campaign was a persistent, long-term operation, significantly compounding the damage to the company's security reputation.
- Notable·
Update: Further investigations revealed that the stolen digital assets were specifically Bitcoin (BTC), with attackers successfully targeting thousands of individual addresses via the firmware bug. Additionally, Toronto-based entrepreneur Jonathan Goodman has been identified as one of the high-profile victims who suffered significant losses in the breach.