
Bitcoin Security Risks Escalate as AI Audit Flags 720 Critical Vulnerabilities
Key Facts
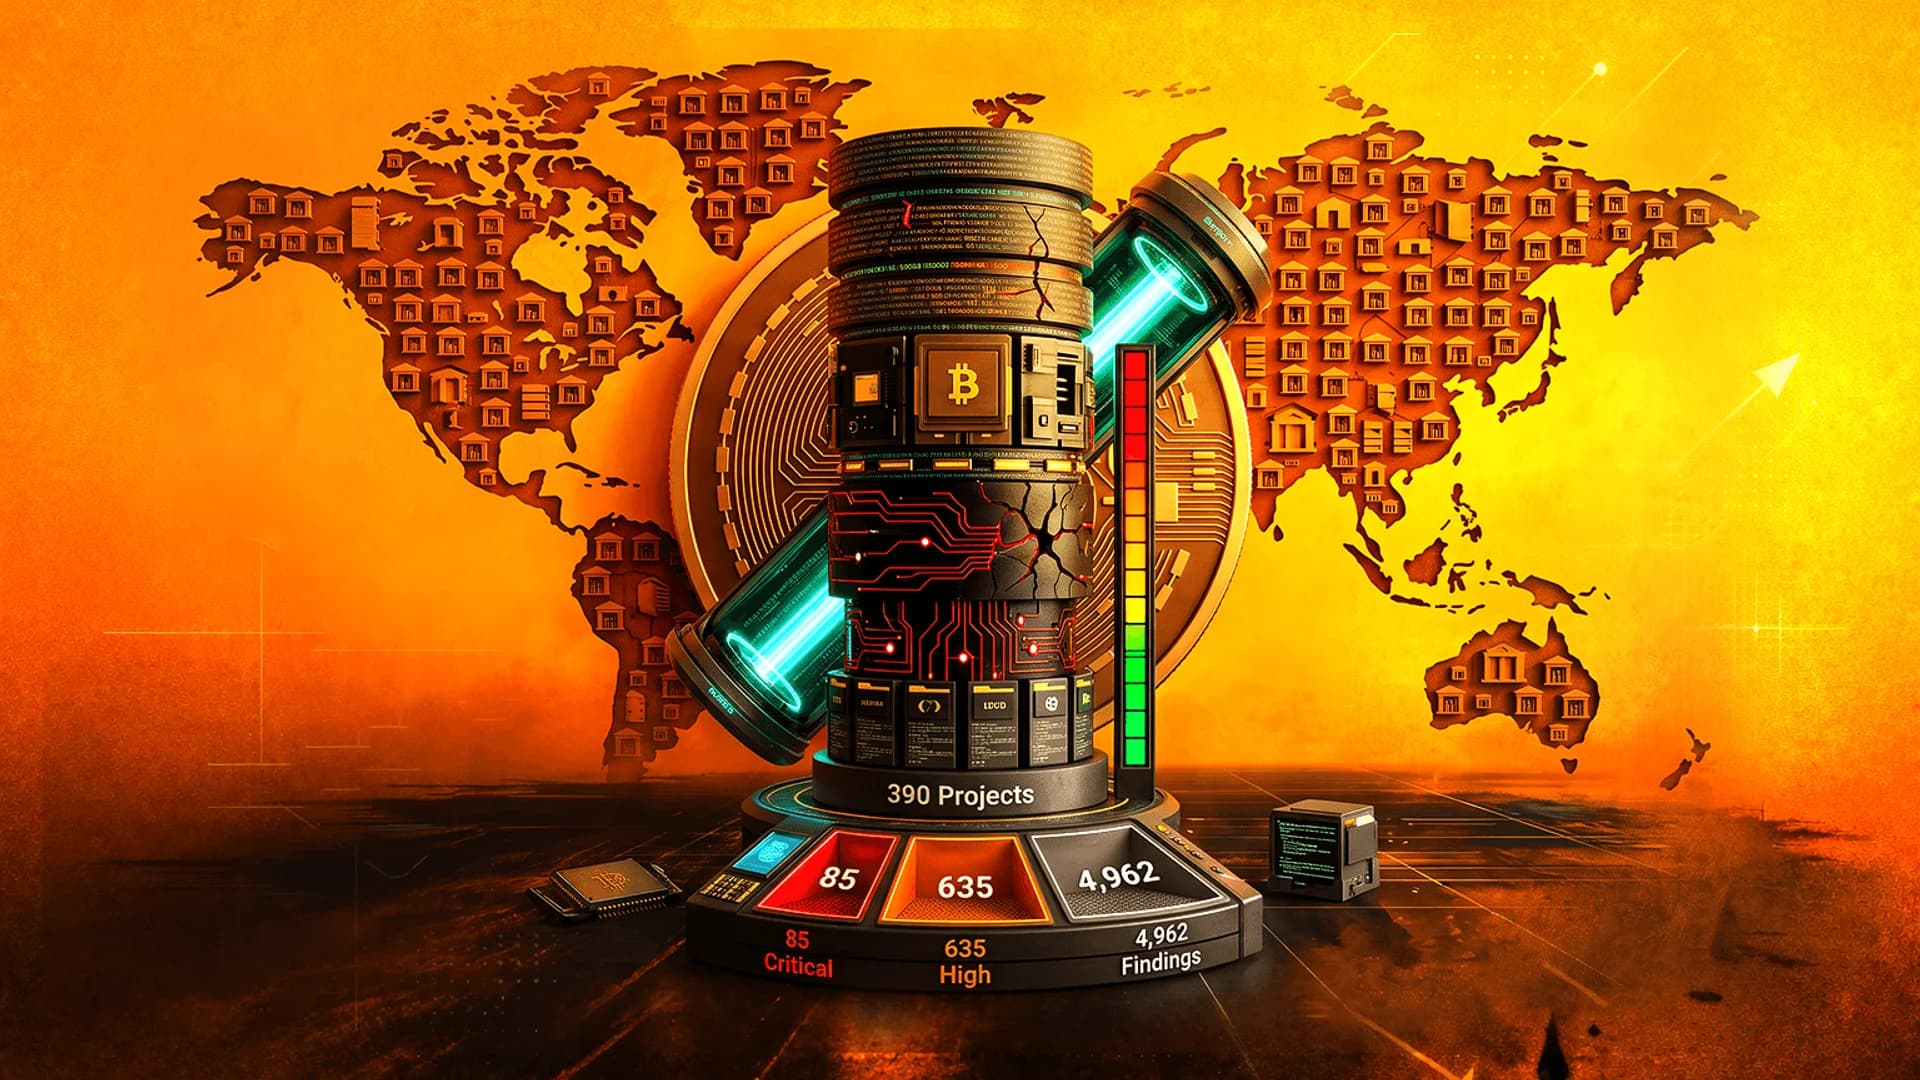
Amid growing reliance on advanced technologies to secure decentralized networks, an expanded AI-powered security audit has revealed a much larger scale of risk within the Bitcoin ecosystem than previously reported. According to the findings, 4,962 security issues were identified across 390 Bitcoin-related projects, with 720 vulnerabilities classified as high severity or critical. This development highlights the escalating security challenges facing digital assets as automated analysis tools uncover deep-seated flaws in software infrastructure.
According to reports from the developers, compute costs for the code analysis reached approximately $10,000 per day to preempt potential exploitation of these vulnerabilities. Analysts noted that the discovery rate averaged one critical vulnerability per hour per person involved, underscoring the urgent need to update cryptographic libraries. The broad scope of affected projects, spanning hundreds of network-related software components, emphasizes the necessity of strengthening security standards across the entire cryptocurrency sector.
Regarding the economic calendar, traders are looking ahead to the release of China's Manufacturing PMI on July 31, 2026, which may impact broader market risk sentiment. Focus remains on how developers will respond to patching the 720 identified critical bugs to maintain network integrity.
Latest Updates · 3
- Notable·
Update: Additional reports reveal that the intensive audit was completed in just 27 hours, involving a team of 16 developers utilizing AI models. Analysts now suggest that the high volume of discovered vulnerabilities primarily highlights a significant challenge in risk triage and classification within these projects, rather than a simple technical security failure.
- Notable·
Update: Additional details from developer Calle revealed that the audit was completed in a record 27.5 hours by a 16-person team. The breakdown of the 720 severe issues has been refined to include 85 critical and 635 high-severity vulnerabilities, highlighting both the efficiency of the scanning tools and the rapid pace of threat detection.
- Notable·
Update: Recent reports reveal that the identification of nearly 5,000 security vulnerabilities occurred within a mere 24-hour window from the start of the audit. This rapid discovery rate highlights the efficiency of the AI tools employed while simultaneously increasing pressure on developers to address these risks immediately.